Alleged Data Breach Targets PhilJobNet, Threat Actor Claims Exposure of 19.2 Million Records
MANILA, Philippines — A threat actor has claimed responsibility for an alleged data breach involving PhilJobNet (philjobnet.gov.ph), the Philippine government's official job portal associated with the Department of Labor and Employment (DOLE), reportedly exposing approximately 19.2 million records containing personal and potentially sensitive information.
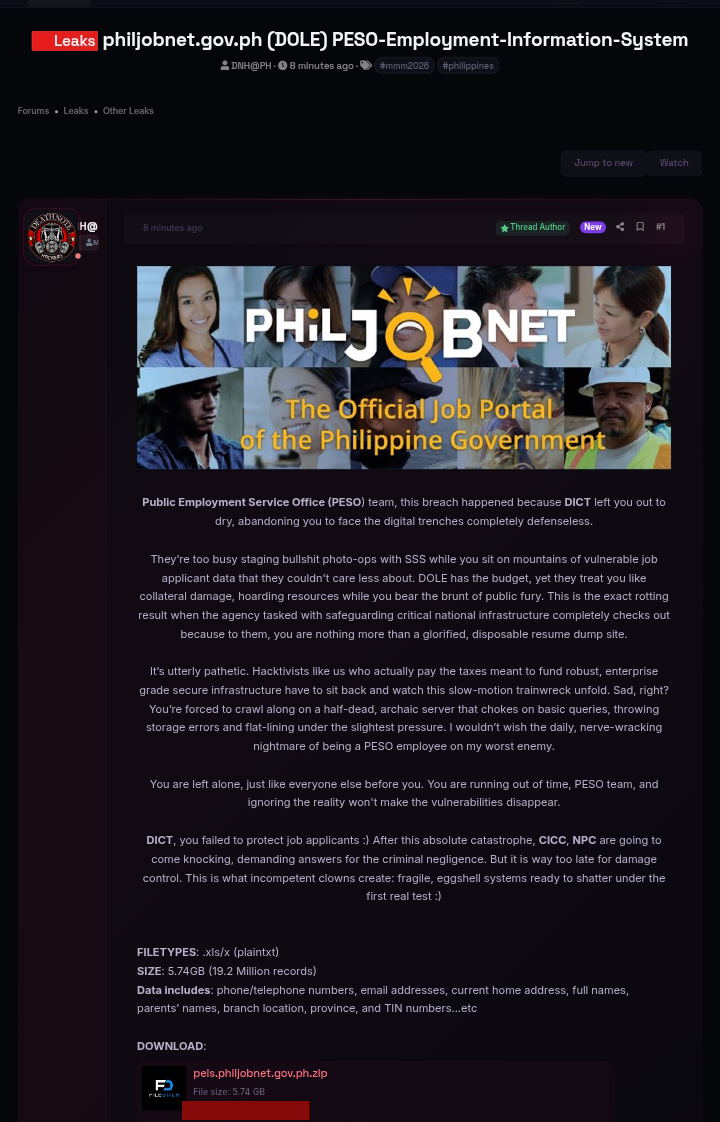
The alleged breach was disclosed in a post published on an underground cybercrime forum, where the threat actor uploaded a sample image of the PhilJobNet platform and advertised a downloadable archive allegedly containing the compromised data.
According to the forum post, the threat actor claims to have obtained approximately 5.74 GB of data, reportedly stored in Excel spreadsheet formats (.xls and .xlsx), as well as plaintext files. The alleged dataset is said to contain approximately 19.2 million records.
The information reportedly includes full names, mobile and telephone numbers, email addresses, current residential addresses, parents' names, branch locations, provinces, and Taxpayer Identification Numbers (TINs), among other personal information.
If authentic, the alleged exposure could present significant privacy and security risks to individuals whose information may have been collected or processed through the employment platform. The combination of personally identifiable information, residential details, contact information, and government-issued identifiers could potentially be exploited for targeted phishing, identity fraud, social engineering, and other fraudulent activities.
In its statement, the threat actor directed criticism toward the Department of Information and Communications Technology (DICT), alleging inadequate protection of government digital infrastructure. The post also mentioned the Cybercrime Investigation and Coordinating Center (CICC) and the National Privacy Commission (NPC), warning that the incident could attract further scrutiny.
However, the claims made by the threat actor, including the reported volume of records and the authenticity of the advertised dataset, have not yet been independently established based solely on the available screenshot. The presence of a download advertisement and the publication of sample material do not, by themselves, confirm the full scope or authenticity of the alleged breach.