Light Rail Manila Corporation Allegedly Targeted by Qilin Ransomware Group
MANILA, Philippines — Light Rail Manila Corporation (LRMC), the private operator of Light Rail Transit Line 1 (LRT-1), has allegedly been targeted by the Qilin ransomware group, following the appearance of the company's name on what appears to be the group's data leak site.
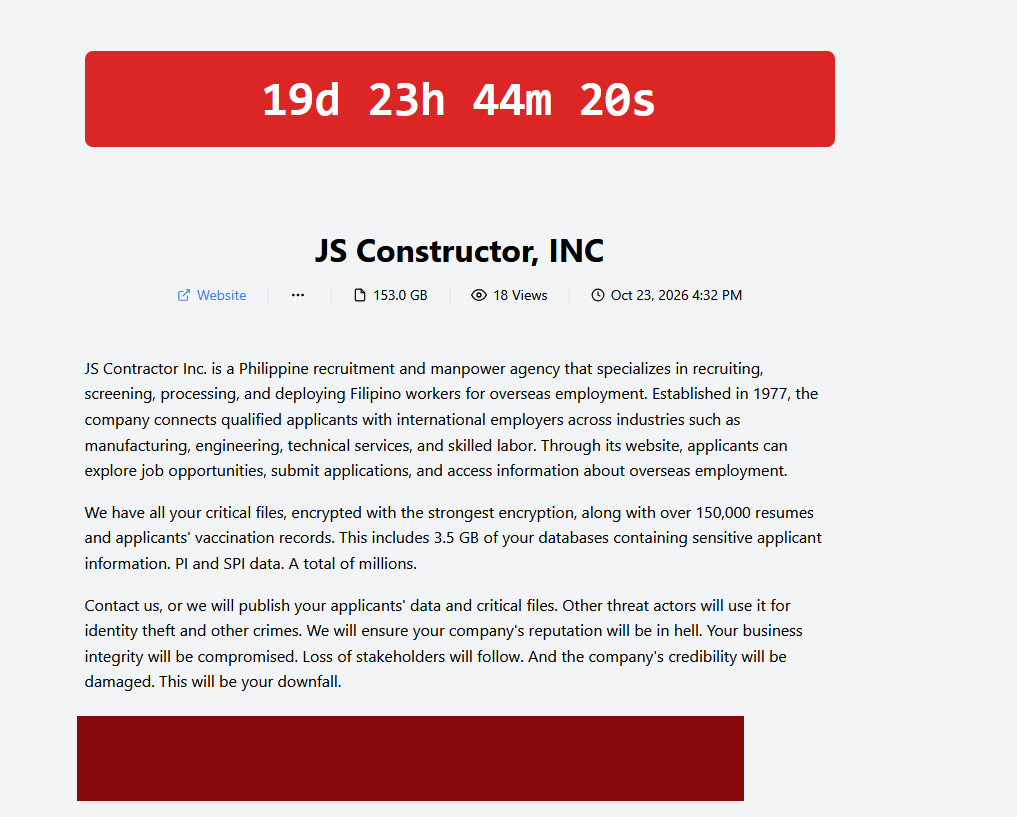
The pos dated October 30, 2026, shows a listing identifying Light Rail Manila Corporation under the Business Services category. The listing also displays a countdown indicating approximately 190 hours and 42 minutes before the purported publication of the allegedly compromised data.
The page reportedly recorded 127 views at the time of observation and showed no uploaded photographs.
Qilin, a known ransomware-as-a-service (RaaS) operation, is associated with cyberattacks involving data exfiltration and double-extortion tactics, wherein threat actors allegedly steal information and threaten to publish it unless their demands are met.
The alleged targeting of LRMC raises concerns over the possible exposure of corporate and operational information. However, the specific nature of the allegedly compromised data, the extent of the reported intrusion, and whether any information was successfully exfiltrated have yet to be independently established.
As of this writing, no verified information has confirmed the incident, and it remains unclear whether Light Rail Manila Corporation has issued an official statement addressing the alleged attack.
Given LRT-1's role in Metro Manila's public transportation network, the reported targeting warrants attention. However, the appearance of the corporation on a ransomware leak site does not necessarily indicate that railway operations, infrastructure, or industrial control systems have been compromised.
The incident remains under verification, pending further information from LRMC and relevant cybersecurity authorities.
DWK Advisory: Ransomware group listings and publication countdowns should be treated as threat actor claims, not definitive proof of a successful breach or data compromise. Independent verification is necessary before establishing the scope and impact of the alleged incident.