Philippine Army Fitness System Breach Exposed by DeathNote Hackers Member “Klammer”
A threat actor identified as Klammer, a member of the hacker group DeathNote Hackers (DNH), has claimed responsibility for breaching the Philippine Army Physical Fitness Test Information System (PA-PFTIS), an online platform used for managing and monitoring the physical fitness test records of Philippine Army personnel.
The claim surfaced through a public post published on a hacking forum, where Klammer shared screenshots allegedly obtained from the compromised system. The screenshots appear to show access to personnel fitness records, administrative dashboards, and internal system functions. Visible information within the screenshots included names, AFP service numbers, ages, sexes, unit assignments, promotion-related records, and physical fitness test data associated with Philippine Army personnel.
https://iili.io/CBLS2vj.png
https://iili.io/CBLS3yx.png
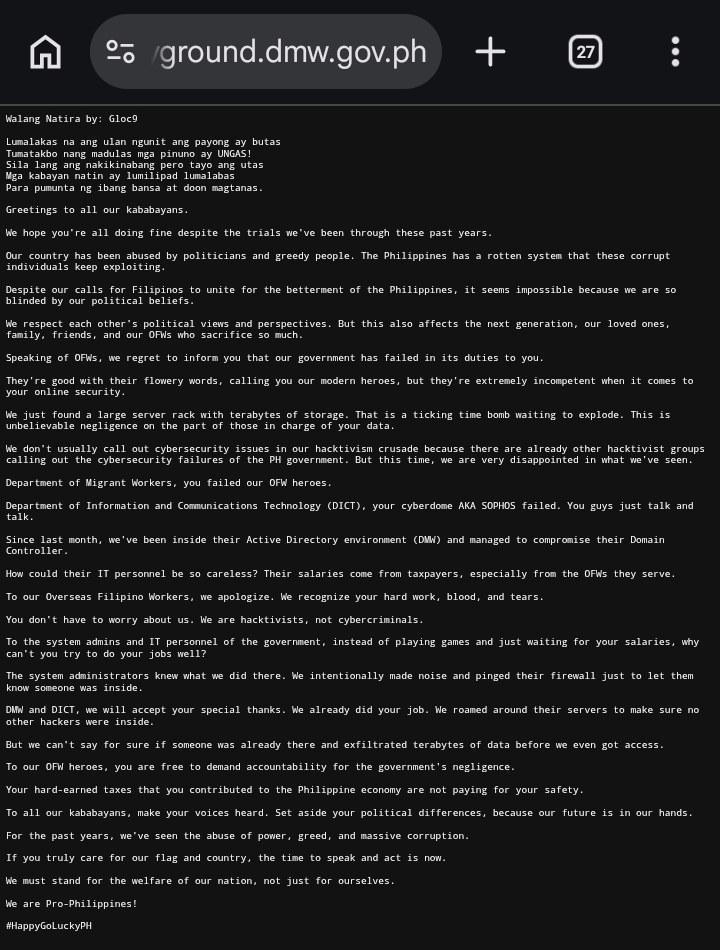
In the public message, Klammer claimed that the compromise was carried out after a previous incident involving government cybersecurity activities. The threat actor stated that the breach would serve as a warning and indicated that additional information could be released if the identified security issues were not addressed.
As part of the disclosure, Klammer reportedly released at least 100 sample personnel profiles allegedly taken from the PA-PFTIS database. The threat actor described the release as a warning rather than a full-scale data dump, claiming that a significantly larger volume of records remained in their possession. Screenshots accompanying the post showed portions of spreadsheets containing what appeared to be military personnel information and fitness assessment records.
Additional images published by the threat actor appeared to show access to the PA-PFTIS web interface, including modules related to registration, activity scheduling, fitness test records, certificate generation, personnel management, and two-factor authentication configuration. The screenshots suggest that the actor may have obtained elevated access within the platform, although the exact method used to gain entry remains unknown.
The PA-PFTIS is designed to facilitate the recording, management, and monitoring of physical fitness test results within the Philippine Army. While there is currently no indication that classified military operational information was exposed, the alleged leak appears to involve personally identifiable information and administrative records belonging to active military personnel.
DeathNote Hackers has previously been associated with various cyber incidents targeting Philippine organizations, government entities, and private-sector systems. Klammer, one of the group's known members, has been linked to several public disclosures and breach claims involving organizations in the country.
As of publication, Philippine Army officials have not publicly confirmed the authenticity of the leaked data or disclosed the full extent of any potential compromise. The scope of the incident, the number of affected personnel, and the validity of the threat actor's claims remain subject to official verification and investigation.