LTFRB Database Leak Claims Exposure of 16 Million Records, 7.7GB of Data
A threat actor has claimed responsibility for a major data breach involving the Land Transportation Franchising and Regulatory Board (LTFRB), alleging the compromise of more than 16 million records contained in approximately 7.7GB of data.
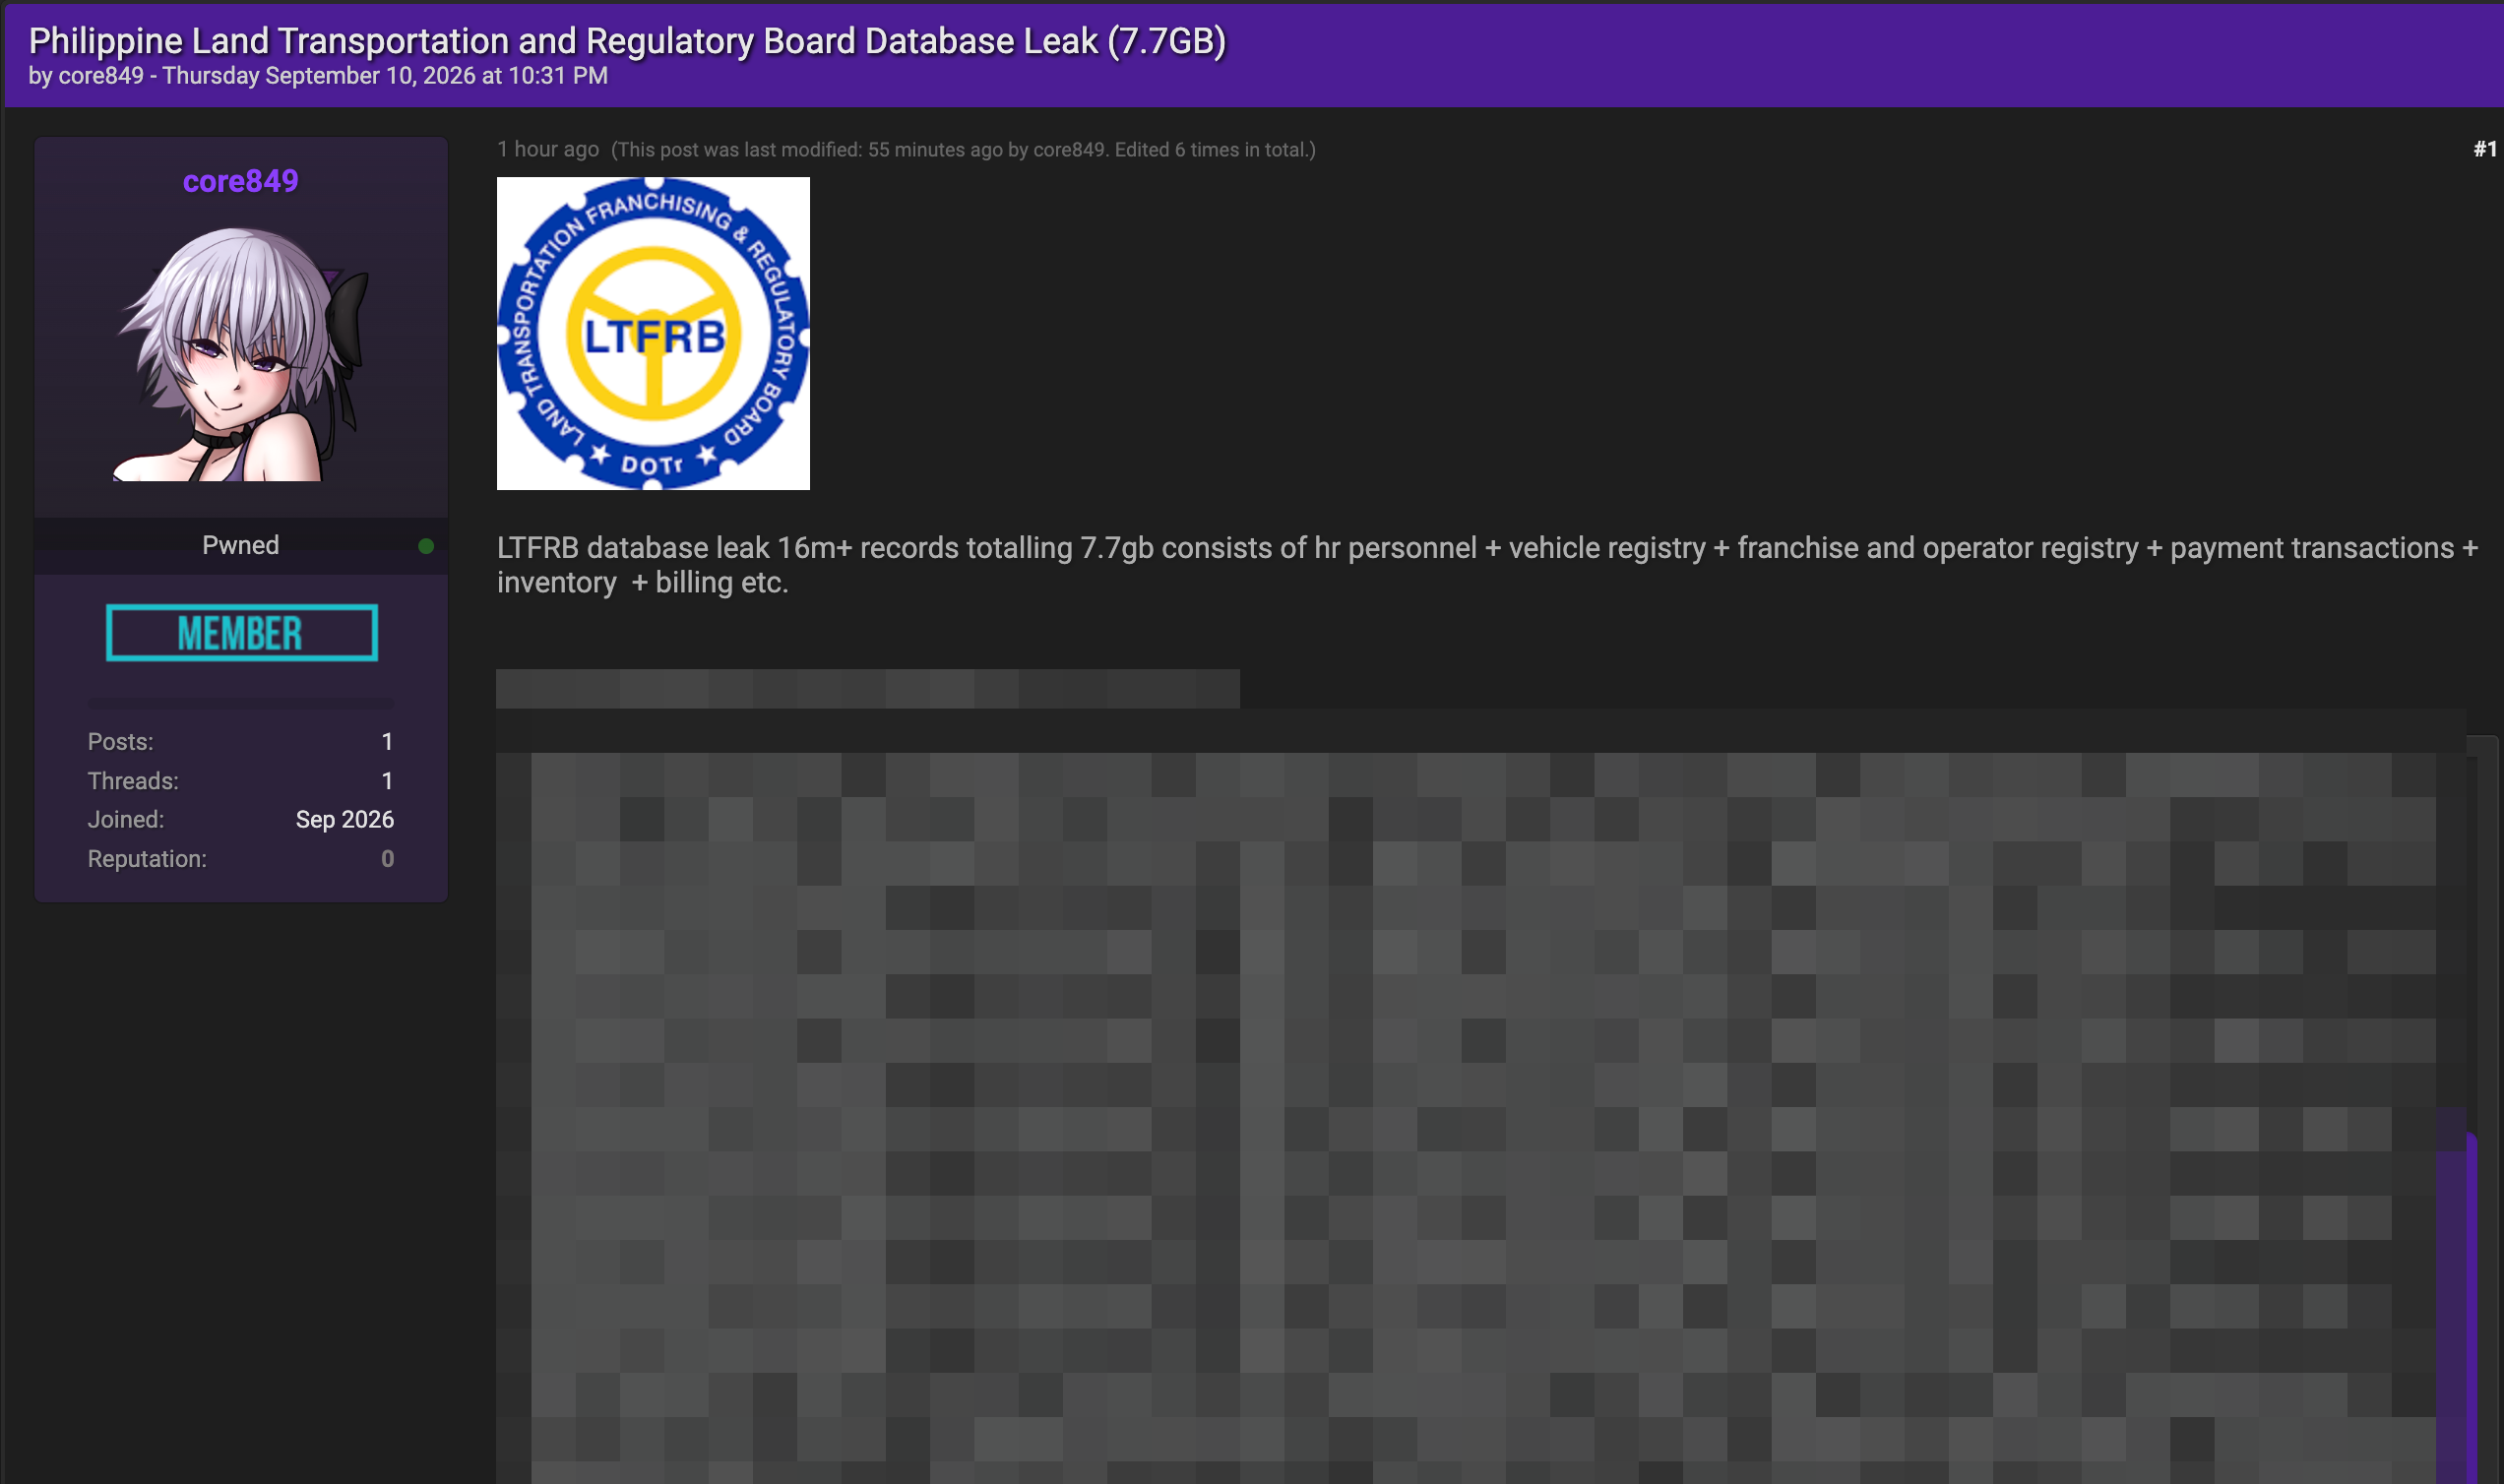
The claim surfaced on a cybercrime forum on September 10, 2026, where the actor identified as “core849” posted an alleged database dump and described it as an LTFRB database leak. The post included the LTFRB logo and claimed that the stolen information came from multiple systems and databases operated by or associated with the transportation regulator.
According to the threat actor, the alleged breach includes human resources (HR) personnel records, vehicle registry information, franchise and operator registries, payment transactions, inventory records, billing information and other related data. The combination of these datasets suggests that the alleged compromise extends beyond a single database or application and may involve several operational systems.
Screenshots accompanying the claim show database files with names including hrm_employee_pds_v2.jsonl, employee-position records, employee salary information, salary-grade data and other HR-related datasets. Another screenshot shows records containing transaction identifiers, application types, payment amounts, dates and user information. These records appear to contain information associated with LTFRB administrative and financial transactions.
HR databases may contain employee-related personal and employment information, while franchise and operator records could potentially contain information concerning public-utility vehicle operators and businesses. Payment and billing records could also provide information about financial transactions conducted through LTFRB systems.
However, the 16-million-record figure and 7.7GB size remain claims made by the threat actor and should not automatically be interpreted as 16 million unique individuals. Database records can include historical entries, duplicate records, transaction logs, system-generated records and multiple entries belonging to the same person or organization.
The alleged incident is also notable because the LTFRB was reportedly targeted in a separate incident in August 2026, when the Quantum Security Group claimed to have breached LTFRB-NCR and released approximately 35GB of data. Public posts from August 17 documented that earlier claim.
However, validation conducted for the present report found that the datasets associated with the August Quantum Security Group incident and the newly claimed 7.7GB leak are completely different. The available evidence therefore does not support treating the September disclosure as simply a redistribution or continuation of the previously reported Quantum Security Group dataset.
This distinction is important because the existence of a previous LTFRB-related breach does not, by itself, establish that the same systems, credentials or databases were compromised in the latest incident. The two datasets should be assessed separately unless further technical evidence establishes a connection.
At the time of reporting, the latest claim should therefore be treated as an alleged breach pending confirmation by LTFRB or relevant Philippine government cybersecurity authorities.